Most security operations centers (SOCs) watch the office around the clock but lack the five OT security capabilities a factory needs: 24x7 OT monitoring, OT detection engineering, OT threat hunting, investigation with operational context and coordination with operations during a response. Without them, an attack on the plant can become a power outage, a production stop or a disclosure the CISO has to explain. Mithryl Systems OT managed detection and response (OT MDR) adds dedicated OT monitoring, investigation and operational coordination to the SOC you already run.
The plant is already your problem. In Fortinet's 2026 survey of more than 700 OT professionals, 60% said the CISO or CIO has ultimate responsibility for OT cybersecurity, and 81% intend to move it under the CISO within 12 months. Operational technology (OT) is the hardware and software that runs physical processes, from controllers to the servers that trip breakers. For each capability below, ask who owns it today.
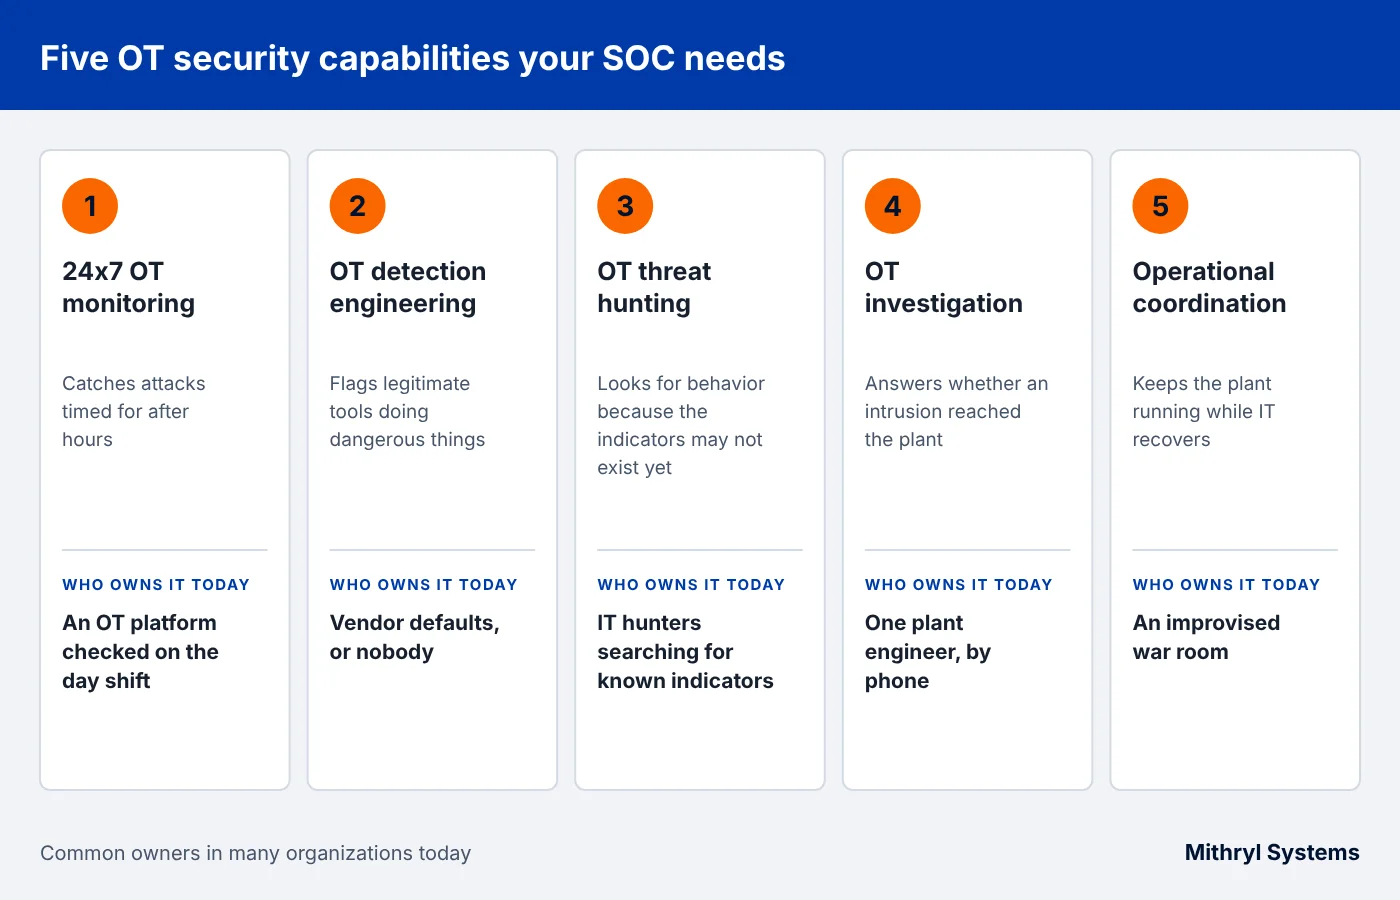
Five OT security capabilities your SOC needs, and who commonly owns each one today
1. Around-the-Clock OT Monitoring Catches Attacks Timed for After Hours
OT monitoring only works if someone who can read industrial traffic is watching when the attack lands, and attackers pick their hours. In April 2022, ESET researchers found malware they named Industroyer2 at a Ukrainian energy company, set to run at 16:10 UTC (7:10 p.m. in Kyiv) on Friday, April 8, to cut power to a region. It spoke IEC 60870-5-104, the protocol grid operators use to send commands to substations.
They also set a wiper, CaddyWiper, to erase some of the company's Windows machines that day. CERT-UA, Ukraine's national response team, said the attack had been prevented.
An IT-only SOC would have seen half of that attack. The wiper lives in its world; substation commands travel in a protocol enterprise tools don't parse. Timing matters: in Sophos's 2026 Active Adversary Report, 88% of ransomware payloads were deployed outside business hours.
Who owns it today? Often an OT monitoring tool that engineering checks on the day shift. Mithryl Systems OT analysts monitor customer environments around the clock, every day of the year.
2. OT Detection Engineering Flags Legitimate Tools Doing Dangerous Things
OT detection engineering is the work of writing rules that separate normal engineering activity from an attack, and in most organizations nobody owns it. Sandworm's October 2022 attack on a Ukrainian utility, documented by Mandiant, shows why.
The attackers reached a hypervisor hosting the utility's supervisory control and data acquisition (SCADA) system, the software operators use to command substations. They ran scilc.exe, a program that ships with the utility's own MicroSCADA software. Mandiant assessed that the commands were probably meant to open circuit breakers, and the attack caused an unscheduled power outage. Two days later, a new CaddyWiper variant hit the IT environment.
To an endpoint tool, a vendor's own program running on a SCADA server looks routine, like an admin console that trips breakers instead of rebooting servers. Mandiant published a detection rule for scilc.exe command execution, the kind of content an enterprise security information and event management (SIEM) platform never ships with.
Today, SIEM rules are written for laptops and the OT platform runs vendor defaults. Mithryl Systems OT detection engineering builds detection logic for industrial protocols, including IEC 60870-5-104, Modbus and DNP3, with detections for unauthorized engineering operations and anomalous control commands.
3. OT Threat Hunting Looks for Behavior Because the Indicators May Not Exist Yet
OT hunting has to start from behavior, because the most dangerous tools may never have been seen before. In April 2022, the Department of Energy, CISA, NSA and FBI warned of a toolkit built to attack Schneider Electric and Omron controllers and OPC UA servers. Dragos named it PIPEDREAM; Mandiant called it INCONTROLLER.
According to the advisory, it could scan for controllers, brute-force passwords, send custom Modbus commands and crash a controller until someone power-cycled it. On Windows workstations, it exploited a vulnerable ASRock driver to run code in the kernel. Dragos assessed it hadn't yet been used for destructive effects, a rare case of an OT attack capability found before use.
Mandiant's guidance was blunt: "indicator-based detections would not be effective," and defenders should "focus their efforts on behavior-based hunting."
Who owns it today? IT threat hunters sweeping for known indicators, with controllers out of scope. Mithryl Systems OT MDR includes continuous threat hunting that draws on customer-specific operational context.
4. OT Investigation Answers the Question Your Disclosure Depends On
When an intrusion hits a company with physical operations, executives first ask whether it reached the plant, and answering takes investigators who understand the plant. In October 2024, American Water Works, the largest regulated water and wastewater utility in the U.S., found unauthorized activity in its networks and disconnected or deactivated some systems.
It took its customer portal offline and paused billing for a time. In a Form 8-K, the company said it believed none of its water or wastewater facilities or operations had been negatively impacted.
Every company with physical operations needs to write that sentence with evidence behind it. That means knowing what the intruder could reach and whether controller or SCADA behavior changed. An IT investigation stops at the boundary.
Who owns it today? Usually one plant engineer, reached by phone, the pattern in Your OT Expert Is Not an Escalation Process. Mithryl Systems analysts investigate every significant event before contacting your team, with asset identification, operational context and impact analysis.
5. Operational Coordination Keeps the Plant Running While IT Recovers
Once an incident is confirmed, security, operations and engineering have to make decisions together, and in most organizations that coordination is improvised. In March 2019, LockerGoga ransomware hit Norsk Hydro, affecting all 35,000 employees in 40 countries, according to Microsoft.
Some of the aluminum maker's roughly 170 plants switched to pen and paper. Executives texted photos of handwritten warning signs to plant managers, and retirees came back to help run paper processes. The cost eventually approached $71 million.
What kept product moving was people who knew which plants could run by hand. Disruption is the usual outcome: in the SANS 2026 State of ICS/OT Security survey, 34% of industrial organizations suffered a cyber incident, and 72% of those incidents disrupted operations.
Today that coordination happens in an improvised war room. During an active incident, Mithryl Systems analysts provide investigation support, forensic analysis, guidance and coordination, following predefined escalation procedures that include security, operations, engineering and, as appropriate, executives. Operations keeps decisions that could affect production.
Who Owns Each OT Security Capability Today
In many organizations, the honest answers look like this.
| Capability | Common owner today | With Mithryl Systems OT MDR |
|---|---|---|
| 24x7 OT monitoring | An OT platform checked on the day shift | OT analysts around the clock |
| OT detection engineering | Vendor defaults, or nobody | Detections for industrial protocols and engineering operations |
| OT threat hunting | IT hunters searching for known indicators | Continuous hunting with current intelligence and operational context |
| OT investigation | One plant engineer, by phone | Investigation before escalation, with impact analysis |
| Operational coordination | An improvised war room | Predefined escalation across security, operations and engineering |
Frequently Asked Questions
Can our IT SOC take on OT alerts, or do we need an OT SOC?
Not necessarily. Your SOC can ingest OT alerts through its SIEM, but acting on them takes OT detection logic and knowledge of what each asset controls. Many Mithryl Systems customers keep their enterprise SOC and rely on Mithryl Systems OT MDR for OT-specific monitoring and investigations.
Who should own OT security, the CISO or operations?
Increasingly, the CISO. In Fortinet's 2026 survey, 60% of respondents said the CISO or CIO has ultimate responsibility for OT cybersecurity, and 81% intend to move it under the CISO within 12 months. Operations should still own decisions that affect production, and Mithryl Systems leaves those decisions with your operations and engineering teams.
How is OT threat hunting different from IT threat hunting?
OT hunting starts from behavior in industrial protocols instead of known indicators. State-built OT tools such as PIPEDREAM may never have been seen before, so Mandiant advised behavior-based hunting over indicator matching.
How fast can we get OT coverage without hiring an OT team?
Mithryl Systems says most organizations begin receiving value within the first few weeks, because the service integrates with the SIEM, endpoint detection and response (EDR), OT monitoring and remote access tools you already have. Onboarding starts from your asset inventory and escalation contacts.
Find Out Who's Watching Your Factory Tonight
Put a name next to each of these five capabilities. If the answer is a dashboard nobody checks after 5 p.m., a vendor rule set or one engineer's cell phone, your SOC is watching the office and hoping the factory is fine.
Mithryl Systems OT MDR adds dedicated OT monitoring, investigation and operational coordination to the SOC you already run. Talk to Mithryl Systems about reviewing your OT monitoring, detection and investigation coverage against these five capabilities.
Sources and Further Reading
- Fortinet, 2026 State of Operational Technology and Cybersecurity Report (June 2026)
- ESET, Industroyer2: Industroyer reloaded (April 12, 2022)
- TechCrunch, Ukraine disrupts attempt by Russian hackers to take down energy provider, reporting CERT-UA's statement (April 12, 2022)
- Sophos, Active Adversary Report 2026
- Mandiant, Sandworm Disrupts Power in Ukraine Using a Novel Attack Against Operational Technology (November 9, 2023)
- U.S. Department of Energy, CISA, NSA and FBI, Joint Cybersecurity Advisory AA22-103A (April 13, 2022)
- Dragos, CHERNOVITE's PIPEDREAM Malware Targeting Industrial Control Systems (April 13, 2022)
- Mandiant, INCONTROLLER: New State-Sponsored Cyber Attack Tools Target Multiple Industrial Control Systems (April 13, 2022)
- American Water Works, Form 8-K (October 7, 2024)
- SecurityWeek, American Water bringing systems back online after cyberattack (October 2024)
- Microsoft, Hackers hit Norsk Hydro with ransomware. The company responded with transparency (December 2019)
- SANS Institute, 2026 State of ICS/OT Security Survey (November 10, 2026)
- Microsoft Learn, Integrations with Microsoft and partner services (Defender for IoT)